TL;DR

Get home appliances delivered free — and shop member deals
- Fast, free delivery on millions of items
- Access to Prime Big Deal Days deals on October 6–7
- Prime Video, Amazon Music and more included
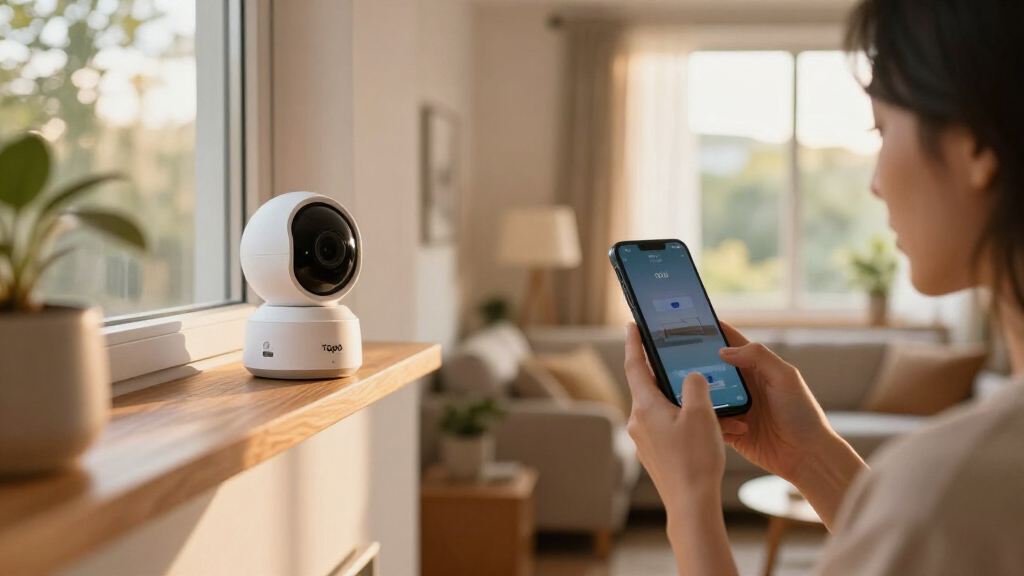
TP-Link has released firmware updates for its Tapo C200 and C120 cameras to fix a high-severity login bypass that could grant administrator access to someone on the same network. A separate flaw that can crash or restart the C200 is also patched; owners should update each camera to its latest firmware.
TP-Link has released firmware updates for its Tapo C200 and C120 cameras to fix a login flaw that could let an attacker on the same network gain administrator access without a password. Security firm OPSWAT reported the vulnerabilities; a separate flaw that can disrupt the C200 is also covered by the updates.
The main issue, tracked as CVE-2026-15315, received a severity score of 8.7. According to OPSWAT researchers Khoi Tran and Thai Do, it lies in the cameras’ HTTPS management interface. A second verification path accepts a value the device provides during login as if it were an authentication response. With a small number of requests, an attacker can obtain an administrator session without a password or an existing session.
That session can expose live video and stored recordings and allow changes to camera settings. OPSWAT said the access could also reach features such as night vision, crying detection and two-way audio when a camera is used as a baby monitor. These are capabilities the researchers described as accessible; the report does not say that attackers have used the flaw in real-world incidents.
A second vulnerability, CVE-2026-15316, has a score of 7.1 and affects the C200, according to the report. An oversized section of encrypted Wi-Fi credential data can cause the camera’s HTTPS service to crash or the device to restart while it recovers. TP-Link’s updates address both vulnerabilities, and the C120 is listed as affected by the login flaw in its V1 hardware version. Owners should install the latest firmware on each affected camera.
What Camera Owners Could Expose
The login bypass matters because an administrator session could provide access to private camera feeds, recordings and settings. For households using cameras to watch children or monitor rooms remotely, unauthorized access could expose intimate activity and enable changes to how the device operates. The impact described by OPSWAT depends on an attacker first being able to reach the household’s network.
That access requirement narrows the reported attack scenario: the vulnerabilities do not, on the information provided, let an outsider simply connect to any camera over the internet. But a person or device already inside a home’s Wi-Fi network—or within a trusted connected environment—could pose a risk. The C200 crash flaw has a different potential consequence: service disruption or a device restart rather than the administrator access associated with CVE-2026-15315.
Installing the manufacturer’s firmware is the direct mitigation identified in the report. Owners should check each camera, since an update to one device does not necessarily update other cameras on the same account or network. The available material does not establish how many devices are affected or whether any were accessed before the fixes.
As an affiliate, we earn on qualifying purchases.
How the Tapo Flaws Were Found
OPSWAT researchers Khoi Tran and Thai Do identified two high-severity vulnerabilities in the Tapo C200 series, according to The Ambient’s report. Their findings concerned the cameras’ management interface and handling of encrypted Wi-Fi credential data. The report says TP-Link subsequently issued firmware updates for the affected models.
The scope differs by flaw. CVE-2026-15315 affects the C200 and, according to TP-Link’s advisory as described in the report, the C120 in its V1 hardware version. CVE-2026-15316 affects the C200 alone. Both flaws require an attacker to be on the same Wi-Fi network or already within a trusted ecosystem, a condition that limits the reported exposure compared with a vulnerability reachable by anyone on the public internet.
The report’s central distinction is between access and disruption: the login flaw can yield administrator privileges, while the separate C200 issue can interrupt the HTTPS service or restart the camera. The supplied source does not include the firmware version numbers, dates of disclosure or a detailed account of TP-Link’s investigation.
““live video, night vision, crying detection and two-way audio””
— OPSWAT researchers Khoi Tran and Thai Do, as reported by The Ambient
security camera with night vision and two-way audio
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Exposure and Update Status
The available report does not say how many cameras are affected, whether attackers have exploited either flaw, or whether any customer data or footage has been accessed. It also does not give firmware version numbers, the exact release date of the patches, or details on whether cameras install updates automatically.
The reported attack path requires access to the same Wi-Fi network or a trusted ecosystem, but the source does not specify every condition under which that access could be obtained. Owners should consult TP-Link’s current advisory or the Tapo app for model-specific instructions, especially for the C120’s V1 hardware version. The source identifies no additional affected C120 hardware versions.
home security cameras for indoor monitoring
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Owners Should Check Firmware
TP-Link has issued updates, and the immediate next step for owners is to check for and install the latest firmware on each Tapo C200 or C120 camera. The C200 update addresses both reported flaws; the C120 update addresses the login bypass covered by CVE-2026-15315, according to the source.
Owners who cannot confirm that an update has installed can check the camera’s device or firmware settings in the Tapo app and refer to TP-Link’s support information for the precise model and hardware revision. The report does not provide a future investigation milestone or say whether further fixes are planned. Any new information about exploitation, affected hardware revisions or firmware availability would clarify the remaining questions.
smart home security camera replacement parts
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Key Questions
Which TP-Link cameras are affected?
The Tapo C200 is affected by both reported flaws. TP-Link’s advisory, as described in the report, lists the Tapo C120 V1 hardware version as affected by the login bypass, CVE-2026-15315.
What could the main vulnerability let an attacker do?
The login bypass could grant an administrator session without a password or existing session, potentially exposing live video and recordings and allowing configuration changes. The reported attack requires access to the same Wi-Fi network or a trusted ecosystem.
Does the separate flaw affect the C120?
No. The report says CVE-2026-15316 affects the C200 alone. It can cause the HTTPS service to crash or the camera to restart after receiving oversized encrypted Wi-Fi credential data.
What should camera owners do?
Install the latest firmware on each affected camera and check TP-Link’s support guidance for the exact model and hardware revision. The source does not provide firmware version numbers or confirm whether updates are installed automatically.
Is there evidence that attackers used these flaws?
The source report does not state that either vulnerability has been exploited in real-world attacks, nor does it report confirmed access to customer cameras or recordings. That status remains unclear based on the information provided.
Source: rss
NFL season / tailgating Picks
team gear
As an affiliate, we earn on qualifying purchases.